Inicio > > Seguridad informática > Application Security in the Age of AI™
Application Security in the Age of AI™

Application Security in the Age of AI™

Stephen R Jordan

39,22 €
IVA incluido
Disponible
Editorial:
SRJ Consulting & Services Publishing
Año de edición:
2026
Materia
Seguridad informática
ISBN:
9798998136917
39,22 €
IVA incluido
Disponible
Añadir a favoritos

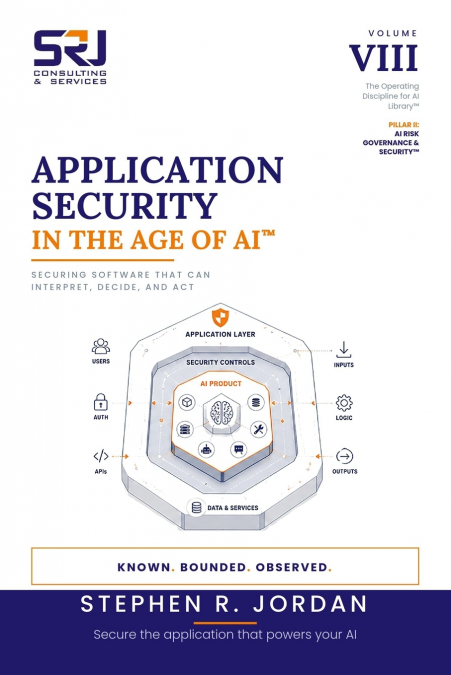
The application passed every security check. Then it approved something it should not have.The expense assistant approved a reimbursement with legitimate credentials, against the legitimate endpoint, with parameters that passed every rule in the schema. It did so on the instruction of a wiki page an employee had edited that morning. Eleven controls had looked at it, and every one reported green.Nobody skipped a check. The checks were reading the code, and the application was reading a wiki page.Not a tooling problem. A limit.An AI application’s behavior is produced at runtime from the model, the prompt, the retrieved context, the tool descriptions, and the memory. None of that is in the artifact your scanner inspects, and any of it can change without a commit. Verifying that behavior beforehand is not merely hard. It is formally undecidable in the general case.If you cannot prove what an AI application will do before it runs, security must also control what it is allowed to do while it runs.For the enterprise that builds its own softwareNot the vendor shipping AI to customers. Not the buyer evaluating someone else’s model. The enterprise with four hundred applications on a register, six hundred and forty actually running, three people in the security function, and an engineering organization that adopted assistants and doubled its merge rate without asking anyone.What you will buildHow it is writtenEvery chapter opens on an operational problem, installs one instrument, and closes with the board question you must answer, the evidence required, the failure pattern that breaks it, and a thirty-day move with a named owner. Chapter 18 sequences the first ninety days.No vendor names anywhere. Every executive-level number carries its source and its denominator in the same sentence. The book also states plainly what it does not solve: three conditions remain open in the research literature, and nothing here closes them.Includes 131 figures, a 133-entry research bibliography, and a twenty-two-instrument appendix available free as working files. Mapped to NIST SP 800-218, the NIST AI Risk Management Framework, ISO/IEC 42001, the OWASP Top 10 for LLM Applications, MITRE ATLAS, and the EU AI Act.Written for CISOs, directors of application security, security architects, and the engineers who build what they secure.Volume VIII of The Operating Discipline for AI Library™. Volume V found the exposure. Volume VI built the program. Volume VII built the product so the exposure is designed out. This Volume secures the applications the enterprise builds for itself.
Artículos relacionados

  • Strategic Data-Based Wisdom in the Big Data Era
    Deanna Klein / John Girard / Kristi Berg
    The ability to uncover, share, and utilize knowledge is one of the most vital components to the success of any organization. While new technologies and techniques of knowledge dissemination are promising, there is still a struggle to derive and circulate meaningful information from large data sets. Strategic Data-Based Wisdom in the Big Data Era combines the latest empirical re...
  • Enterprise Service Computing
    Robin G. Qiu / Robin GQiu
    ...
  • Harnessing Knowledge Dynamics
    Mark E. Nissen / Mark ENissen
    ...
  • Effective Cybersecurity Operations for Enterprise-Wide Systems
    Cybersecurity, or information technology security (I/T security), is the protection of computer systems and networks from information disclosure; theft of or damage to their hardware, software, or electronic data; as well as from the disruption or misdirection of the services they provide. The field is becoming increasingly critical due to the continuously expanding reliance on...
    Disponible

    248,86 €

  • IT for Business
    John Young
    IT for Business: A Student’s Guide to the Technology of Business provides readers with a comprehensive understanding of the role and application of information technology in the business world. Each chapter in the book focuses on a different aspect of IT as it relates to business. The opening chapter sets the stage by discussing the importance of developing a keen understanding...
  • Evolution of Cross-Sector Cyber Intelligent Markets
    Eugene J. Lewis
    In today’s digital age, cyber threats have become an ever-increasing risk to businesses, governments, and individuals worldwide. The deep integration of technology into every facet of modern life has given rise to a complex and interconnected web of vulnerabilities. As a result, traditional, sector-specific approaches to cybersecurity have proven insufficient in the face of the...
    Disponible

    275,51 €

Otros libros del autor

  • The AI IT Security Implementation & Strategy™
    Stephen R Jordan
    You ran the AI security audit. You have the model inventory, the non-human identity count, the vendor map, and the data flows. The audit committee accepted it. Then you walked back to your desk and realized the environment it describes changes every week. Someone deployed an agent on Tuesday. A vendor activated an AI feature inside a product you already own on Wednesday and did...
    Disponible

    41,67 €

  • The AI IT Security Audit™
    Stephen R Jordan
    You built a real security program. Patch cycles on schedule, zero trust implemented correctly, incident response tested under pressure. Then AI agents, MCP servers, embedded vendor features, and autonomous tools walked into your environment faster than your operating model could absorb them. That is not a failure of effort. It is a failure of speed. Now a question is forming, f...
    Disponible

    39,05 €

  • The AI Efficiency & Process Optimization™
    Stephen R Jordan
    Governance identifies what must change. The optimization work changes it.Most AI governance work ends at the risk register. The findings get documented, the target state gets approved, and then nothing moves. Projected labor savings stay projected. Usage climbs, dashboards glow, and the CFO still cannot defend the ROI number on the slide.The AI Efficiency and Process Optimizati...
    Disponible

    37,51 €

  • The AI Risk & Governance Review™
    Stephen R Jordan
    Somewhere ahead of you, someone with authority will ask you to prove your AI is governed.It could be an acquirer in diligence, a regulator opening an inquiry, an auditor in fieldwork, or your own board in a moment that does not feel quiet. The question is the same in every version. The companies that can answer it produce a signed document. The companies that cannot improvise a...
    Disponible

    37,45 €

  • The AI Readiness & Performance Assessment
    Stephen R Jordan
    Nobody knows if the AI in your business is working. Including you.It’s drafting your emails, supporting your decisions, and shaping the work that goes to your clients. It’s running inside your tools, your vendors’ platforms, and your employees’ personal accounts. None of it was governed the way you govern hiring, finance, or compliance. You’ve been signing off on AI for months ...
    Disponible

    19,81 €